Authentication
EIGRP (Enhanced Interior Gateway Routing Protocol) IPv6 Authentication is a crucial security feature that ensures the integrity and authenticity of routing information exchanged between EIGRP routers in an IPv6 network. This mechanism helps prevent unauthorized routers from injecting false routing updates and protects against potential threats such as man-in-the-middle attacks. To implement IPv6 authentication in EIGRP, administrators configure authentication keys using the 'ipv6 authentication key-chain' command and associate them with specific interfaces or interfaces participating in the EIGRP process. Key chains consist of multiple cryptographic keys, and routers within the EIGRP domain must share the same key chain to successfully authenticate and exchange routing updates. MD5 is a commonly used algorithm for securing EIGRP IPv6 updates. By deploying IPv6 authentication, network administrators enhance the overall security posture of the EIGRP routing protocol, ensuring that routing information remains trustworthy and unaltered throughout the network.
Lab:
Disclaimer
This Configuration Guide is designed to assist members to enhance their skills in particular technology area. While every effort has been made to ensure that all material is as complete and accurate as possible, the enclosed material is presented on an Dzas isdz basis. Neither the authors nor Forum assume any liability or responsibility to any person or entity with respect to loss or damages incurred from the information contained in this guide. This configuration guide was developed by Forum. Any similarities between material presented in this configuration guide and any other material is completely coincidental.
Cisco IOS Software, Linux Software (I86BI_LINUX-ADVENTERPRISEK9-M), Version 15.2(4)M1, DEVELOPMENT TEST SOFTWARE
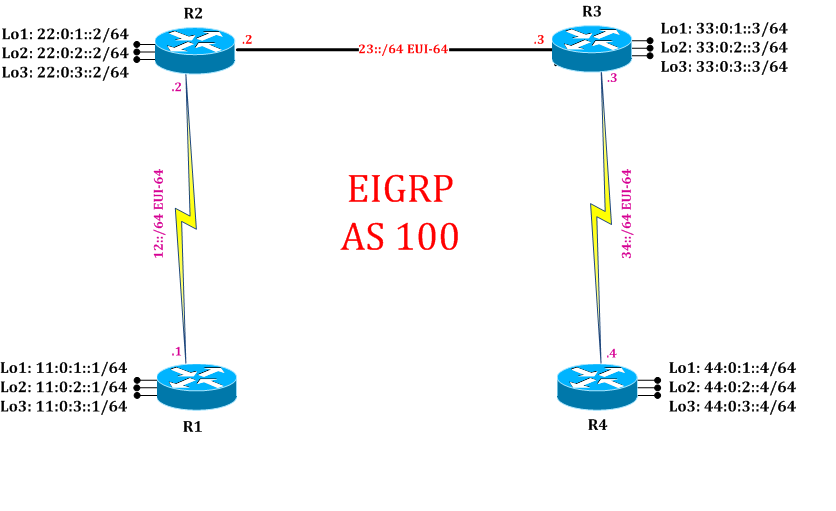
Task 1: Configure IPv6 EIGRP Authentication
Step 1: In the configuration mode of router configure create Key chain and assign key
R1:
key chain akbar	  //creating a key chain with name akbar
key 1			  //selecting a key 1
key-string cisco	//assigning a key-string by which it will authenticate with neighbor, which should be same on both the side
exit
```


**Step 2:**	Enter the interface where authentication is required and select the encryption mode
R1: interface serial 2/0 ipv6 authentication mode eigrp 100 md5 //selecting encryption mode MD5 ipv6 authentication key-chain eigrp 100 akbar //selecting key-chain in which key 1 is selected by which it will authenticate exit
**Step 3:** Enable IPv6 EIGRP authentication on both the neighbors
R2: key chain birbal key 1 key-string cisco exit interface serial 2/0 ipv6 authentication mode eigrp 100 md5 ipv6 authentication key-chain eigrp 100 birbal exit
**Task 2:  Verification:**

**Step 1:**	Verification of authentication by following command:
R1#show running-config // to display the contents of the currently running configuration file key chain akbar key 1 key-string cisco ! interface Serial2/0 ipv6 authentication mode eigrp 100 md5 ipv6 authentication key-chain eigrp 100 akbar
R2#show running-config key chain birbal key 1 key-string cisco ! interface Serial2/0 ipv6 authentication mode eigrp 100 md5 ipv6 authentication key-chain eigrp 100 birbal serial restart-delay 0
**Step 2:** Verify IPv6 EIGRP neighborship by following command:
R1#clear ipv6 eigrp neighbors
R2#clear ipv6 eigrp neighbors //will flush current IPv6 OSPF process and initiate fresh IPv6 OSPF process
R1#show ipv6 eigrp neighbors EIGRP-IPv6 Neighbors for AS(100) H Address Interface Hold Uptime SRTT RTO Q Seq (sec) (ms) Cnt Num 0 Link-local address: Se2/0 11 00:01:31 12 100 0 10 FE80::A8BB:CCFF:FE00:100
R2#show ipv6 eigrp neighbors EIGRP-IPv6 Neighbors for AS(100) H Address Interface Hold Uptime SRTT RTO Q Seq (sec) (ms) Cnt Num 0 Link-local address: Se2/0 11 00:01:31 12 100 0 10 FE80::A8BB:CCFF:FE00:100 1 Link-local address: Et0/0 14 00:01:29 5 100 0 6 FE80::A8BB:CCFF:FE00:300
IPv6 EIGRP neighbors will authenticate with key and if key matches, IPv6 EIGRP neighborship will be formed. Fresh EIGRP neighborship can be verified inIPv6 EIGRP neighbor table